Access Vault
Shared logins, API keys, and license keys, encrypted at rest with a dedicated key, scoped to teams and clients, with every reveal written to an audit log.
- AES-256-GCM encryption with a vault key separate from the rest of the app
- Per-team edit and log-view permissions
- Password versioning so a rotated credential keeps its history
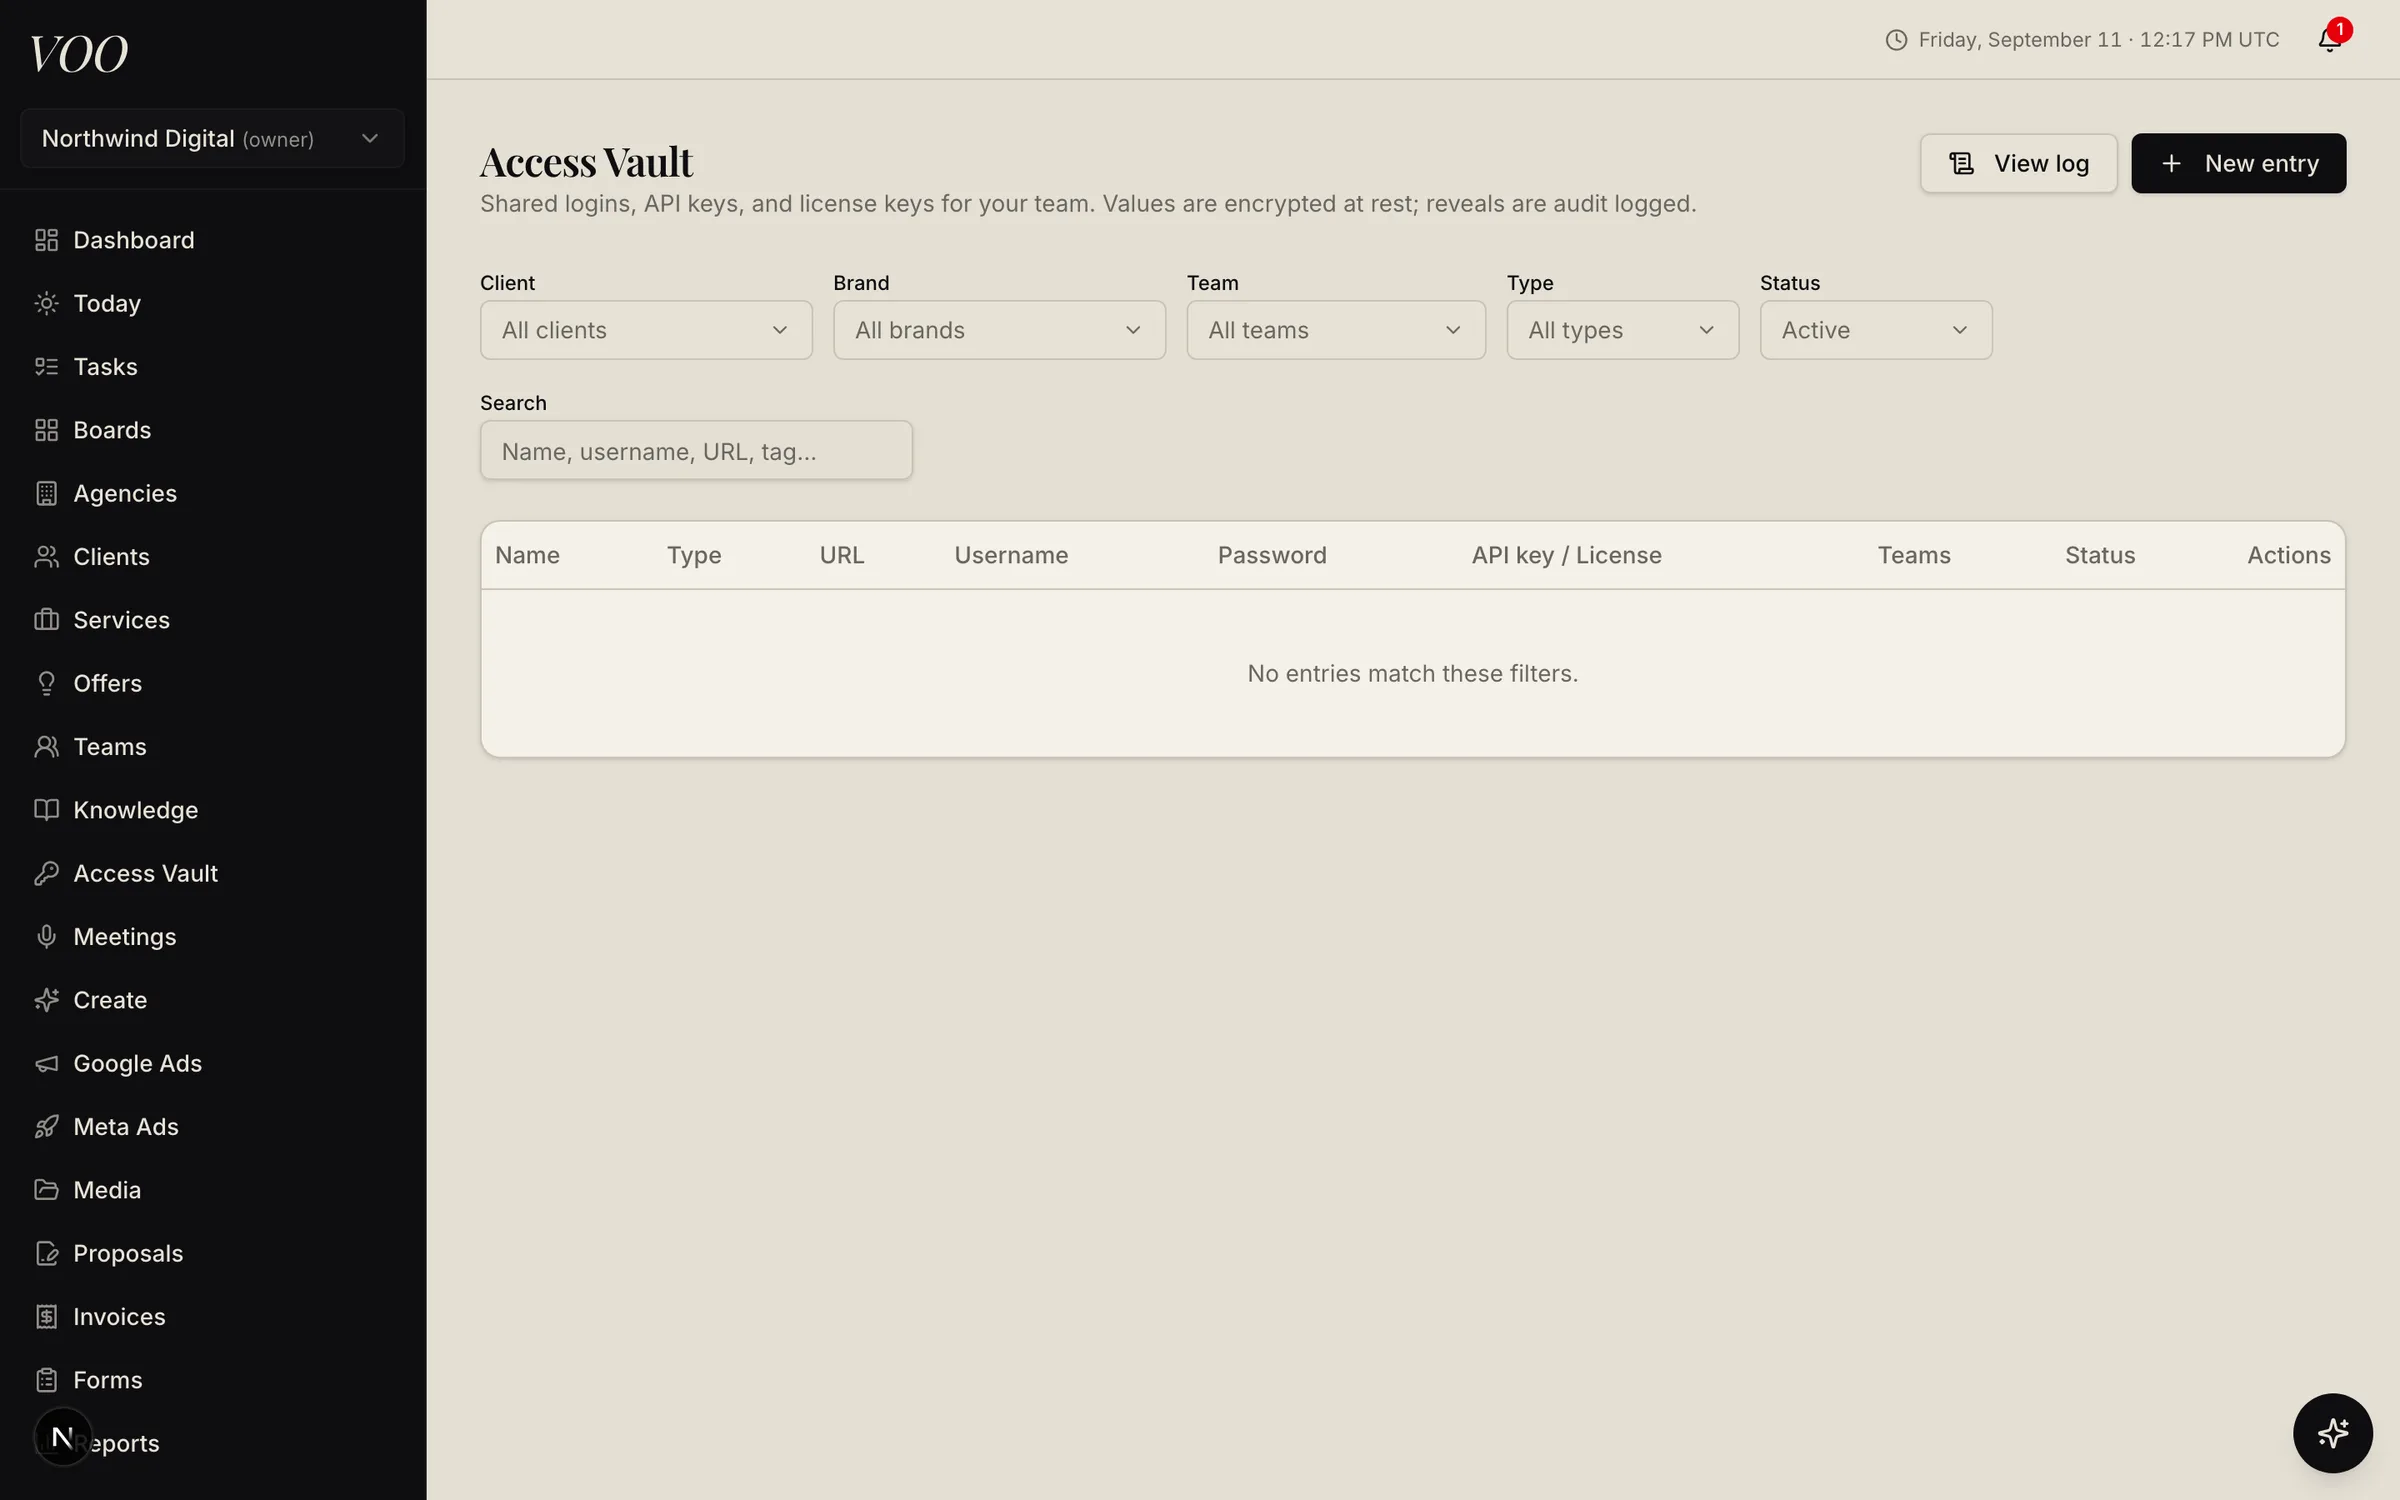
Agencies hold hundreds of client credentials. Voo gives them one home with the controls an auditor expects: a dedicated encryption key, permissions by team, an audit log of every reveal, and version history when a password is rotated.
Entries attach to the client and brand they belong to, so the right people find them from the client record, and offboarding a client shows exactly what needs revoking.